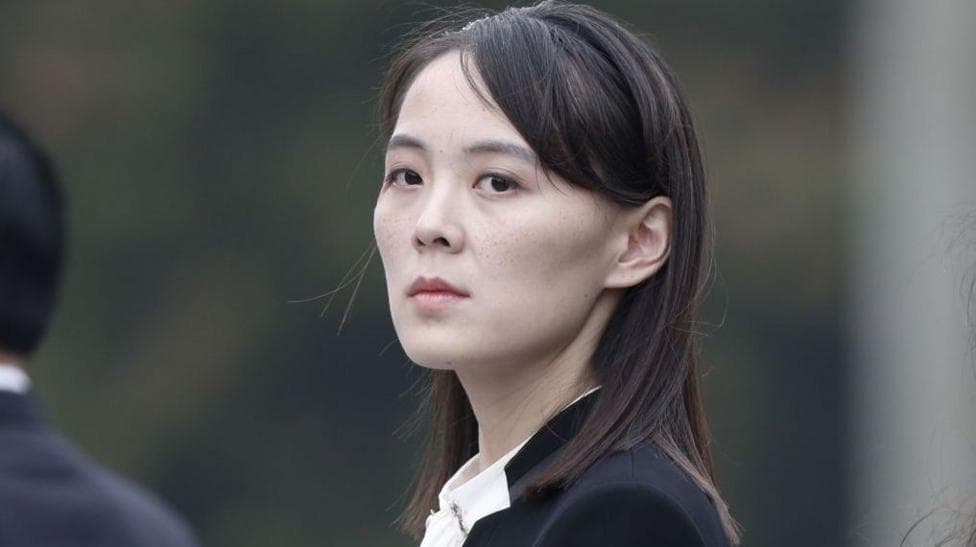
North Korea has firmly rejected allegations that it orchestrated a record $6.3bn (£4.7bn) theft from cryptocurrency exchange Binance, characterizing the accusations as an "absurd rhetoric" and a political attack. Kim Yo-jong, a senior official and sister of leader Kim Jong Un, issued a statement on Tuesday dismissing the claims as a "sinister attempt" by the United States to harm the country's international standing. According to BBC News, the US Federal Bureau of Investigation, the Secret Service and cybersecurity analysts have attributed the attack to North Korean state-backed operatives, describing it as the largest cryptocurrency heist in history.
Investigators have identified the perpetrators as TraderTraitor, a state-sponsored hacking unit also known as the Lazarus Group. The same group was previously blamed for a then-record $1.5bn theft from crypto exchange Bybit in 2025. The FBI has requested that industry partners assist in blocking transactions tied to cryptocurrency accounts connected to the group.
Kim Yo-jong, who serves as director of North Korea's General Affairs Department, characterized the allegations as part of a broader pattern of unfounded accusations.
"The US has made a trite provocation of linking it with the Democratic People's Republic of Korea again,"she stated.
"It is a grave political provocation against the DPRK that the US misleads the international public opinion as if all the cyber crimes in different parts of the world are our deeds,"she added. Pyongyang has consistently denied responsibility for numerous major cyber attacks attributed to it by Western authorities.
What evidence links North Korea to the attack?
Multiple cybersecurity and law enforcement agencies have presented technical evidence connecting North Korean actors to the breach. The FBI alert identified 608 Ethereum addresses, 19 Bitcoin addresses and one Solana address linked to proceeds of the theft. Blockchain analysis firm Elliptic has estimated the total theft at $6.43bn across 11 blockchains, with $2.85bn having been frozen or seized on-chain.
Binance's initial investigation pointed to a compromised DevOps engineer's laptop as a potential entry point, though a later update indicated investigators had found additional points of breach. The attackers employed sophisticated money-laundering techniques, including never-before-seen automated systems designed to obscure the movement of stolen assets across multiple blockchain networks.
How is Binance responding to the theft?
Binance has committed to covering all customer losses from its own reserves, though legal experts have questioned whether such guarantees are binding. The exchange initially suspended deposits and withdrawals while conducting comprehensive security checks. When Binance reopened withdrawals in phases on 1 November, it processed $4.649bn in withdrawals and $1.01bn in deposits during the first nine and a half hours, representing a net outflow of approximately $3.64bn. The company has stated that it had covered about $6bn of the stolen assets, with the remaining tokens being less liquid and potentially requiring longer to source.
The exchange has indicated it would restore additional services in phases following completion of security checks. A detailed technical postmortem of the breach remains pending as the investigation continues. Binance has largely focused its public communications on the technical aspects of the breach and measures taken to protect users going forward.
What happens next?
Binance has committed to restoring additional services in phases after security checks are completed. The detailed technical postmortem was still pending as of the company's latest update. Global regulators are intensifying scrutiny of cryptocurrency exchanges in response to the incident, while the FBI continues to work with international partners to track and recover stolen funds linked to North Korean actors.